Repository navigation
✨ Make project discovery and upload destinations explicit - #395
Merged
Merged
Conversation


Keep account reads independent of checkout upload credentials, recover saved
user sessions, and make project discovery and destination selection explicit.
Verify upload targets before cloud writes and exercise the workflows through
the built CLI and real terminal prompts.

Vizzly - Visual Test ResultsCLI Reporter - Waiting for buildNo builds received yet for this pull request. CLI TUI - 3 changes need review
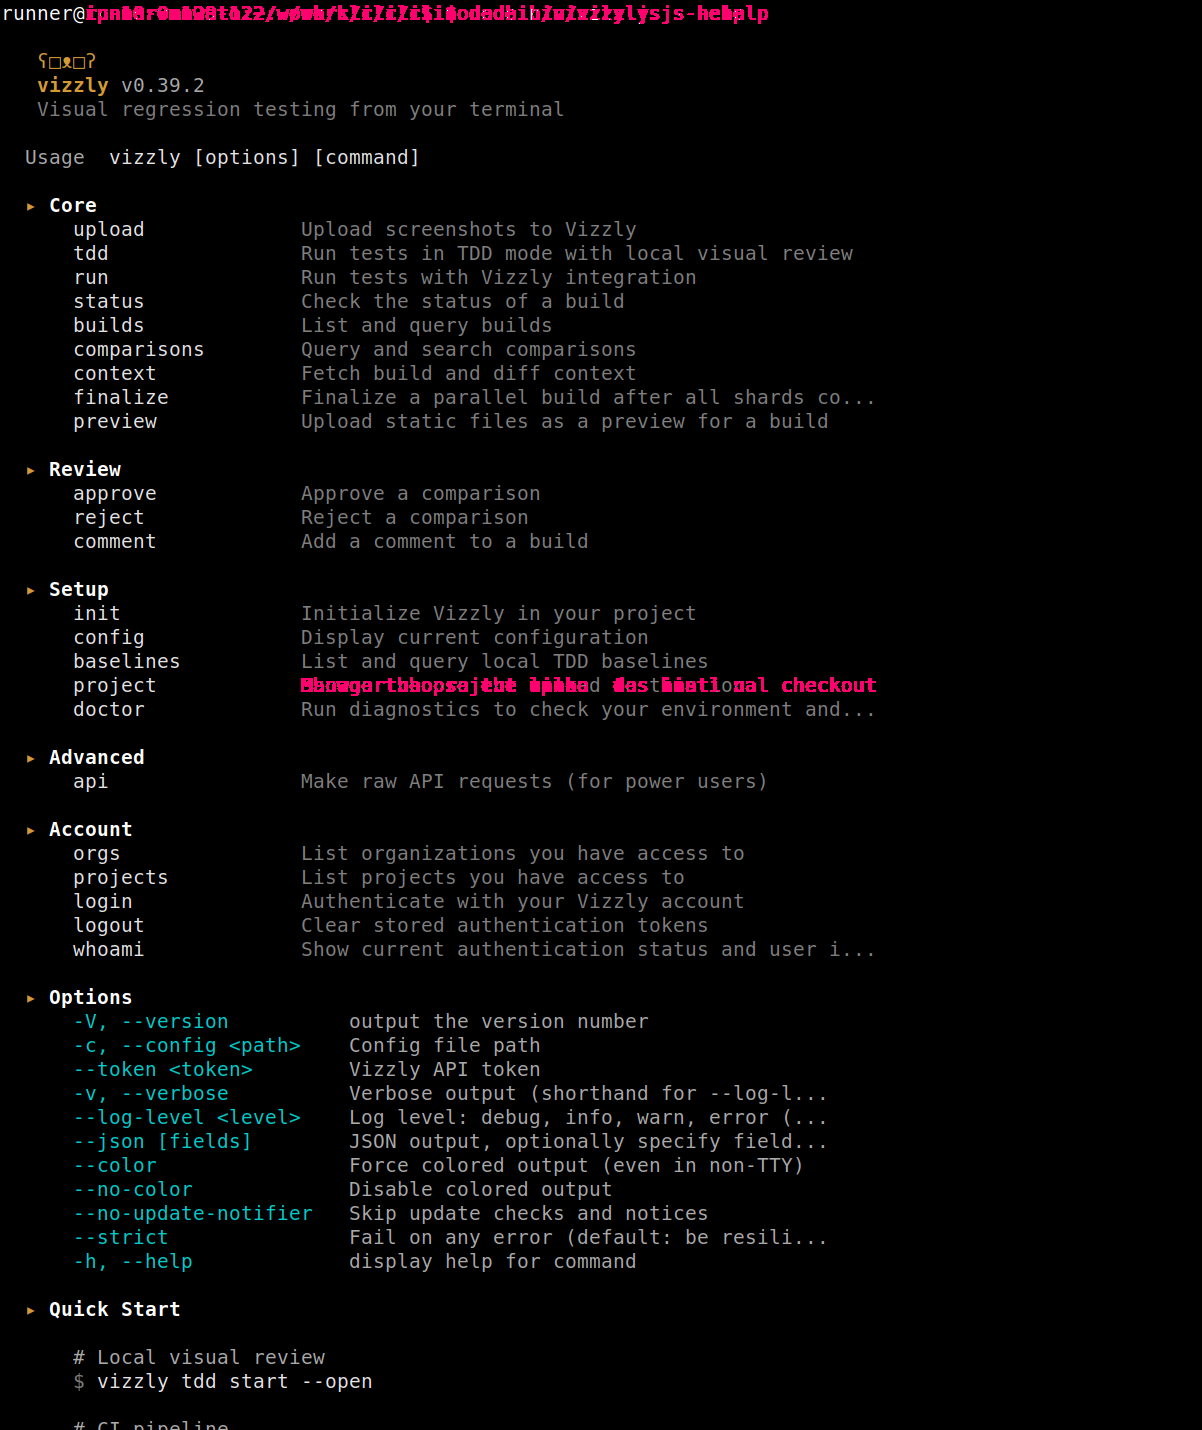
Meaningful diffs needing review (3)vizzly-invalid-command · 1202×578 · 1.5% diff vizzly-help · 1202×1430 · 0.6% diff vizzly-tdd-help · 1202×578 · 1.5% diff
|

Robdel12
added a commit
that referenced
this pull request
Nov 4, 2026
Builds on the project discovery work merged in #395.

## Why

Signing in should be enough to use Vizzly within the permissions the
user grants. Requiring another project credential for uploads made a
valid login feel incomplete, while shared refresh state could make
simultaneous CLI processes invalidate one another.

## Approach

Save consented sessions by API origin, use native credential storage
where available, and coordinate refresh across processes before
rereading the saved successor. Persist refresh uncertainty before
rotation so a dropped response, process exit, or failed save cannot
cause a later command to replay a consumed token. Login supports
explicit scope requests and headless terminals; whoami and permission
errors report the actual grant. Selected-user failures never switch
identities, while explicit CI tokens remain authoritative.

Project linking now saves the checkout destination without minting
credentials. The same selected session reaches uploads, run screenshot
forwarding, finalization, previews, and reporter cloud reads through
supported SDK routes. Build-only uploads work without read permission,
and submitted generic writes are not replayed after authentication
failures.

## Evidence

The full CLI suite passed 1,884 tests with six skips; the reporter
browser suite passed 98 journeys with two skips. Build, published types,
lint, formatting, and architecture checks passed. Additional local
end-to-end verification used the real API for browser-approved login,
four concurrent CLI processes sharing one refresh, user/token build
attribution, read-only rejection before writes, a build-only run with
screenshot forwarding and finalization, isolated logout, and a committed
refresh with a dropped response whose successor remains valid because
the later CLI process refuses replay. The production review also covers
durable uncertain-refresh recovery through real HTTP, disk reload, and
fresh CLI processes. Review covered process-owner death, repeated expiry
windows, lock collisions, bounded authentication requests, and safe JSON
projections.

## Rollout

Release alongside the scoped-session API contract. Existing generic
logins require one fresh browser consent; they are not silently
upgraded. Project-token CI remains supported. Custom VIZZLY_HOME
directories use isolated credential files by default. The duplicate
authentication guide is removed; the README and command help retain the
user workflow.
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Why
Finding a project and reading its builds could use different credentials. A checkout's upload token could hide projects available to the signed-in user, and expired saved access tokens were discarded before refresh could recover the session. This made account browsing look like it required relinking the checkout.
Approach
Keep account browsing separate from the checkout's upload destination. Cloud reads share explicit
--auth auto|user|tokenselection, report credential scope, and recover the selected saved login with one refresh budget. Explicit token settings now take precedence consistently in organization and project discovery. Raw API writes remain unreplayed; review decisions retain their existing retry with an unchanged, server-deduplicated command ID.project linkoffers a paged project picker that guided setup also uses.project statusdistinguishes the configured project from the effective token destination, and run/upload verify that destination before creating a build or sending screenshots. Browsing another project leaves the upload binding unchanged.Discovery and build lists consume the current SDK
metacontract while preserving CLI JSONpaginationand the 250-result cap through bounded API pages. Baseline build selection uses that same contract. Help and documentation connect discovery, scoped browsing, and upload setup.Evidence
Built CLI and real-terminal workflows cover account browsing across projects, pagination beyond 50 results, refresh success/rejection/server failure, picker cancellation, unchanged bindings, wrong-destination rejection, and token-only CI uploads. Review coverage follows actual CLI outcomes instead of mocked internal calls.
The full suite passed with 1,917 tests passing and six skipped. Build, architecture, lint, formatting, and published type checks also passed.